The Unauthorized Stack: How Business Units Are Quietly Building Infrastructure Outside IT's View
Somewhere in your organization, a department that is not IT is running infrastructure that your security team has not reviewed, your compliance function has not assessed, and your operations team cannot support. This is not speculation. It is a condition that exists, with varying degrees of severity, in the majority of US enterprises operating today.
The phenomenon has acquired several names over the years — shadow IT being the most common — but the terminology has not kept pace with the scale of what is actually happening. The image of a rogue employee spinning up a personal cloud account to avoid IT ticket queues remains the popular conception. The reality, in 2024, is considerably more consequential: entire business units deploying multi-service cloud environments, building production data pipelines, and operating customer-facing integrations on infrastructure that exists entirely outside central IT governance.
Understanding why this is happening requires honest engagement with the failures that produced it.
Why Departments Stop Waiting for IT
Centralized IT organizations in large enterprises operate under structural constraints that make them genuinely difficult to work with for business units operating at modern speed. Procurement cycles that span quarters. Change management processes that require weeks of lead time for configuration adjustments. Architectural review boards that interpret every request through the lens of enterprise standardization rather than departmental need.
These constraints exist for legitimate reasons. Standardization reduces operational complexity. Centralized procurement generates volume discounts. Change management prevents the kind of uncoordinated modifications that produce cascading failures. The problem is that these benefits accrue at the enterprise level while the costs are borne disproportionately by the business units waiting for approvals.
A marketing analytics team that needs a new data environment to support a campaign launching in three weeks does not have the option of waiting eight weeks for an infrastructure provisioning request to clear the queue. A finance department that requires a specific integration capability that central IT's standard toolset does not support cannot defer the business requirement while an architectural exception process runs its course. These teams make a rational decision: they find another way.
The availability of cloud services has made that other way accessible to anyone with a corporate credit card. AWS, Azure, and Google Cloud have reduced the technical barrier to infrastructure deployment to near zero for teams with sufficient technical literacy. The result is that the organizational friction which once prevented shadow infrastructure from reaching production scale no longer functions as a meaningful constraint.
The Security Surface Nobody Is Managing
Every business unit operating outside IT governance is, by definition, operating outside the security controls that IT governance enforces. This includes identity and access management standards, encryption requirements, network segmentation policies, vulnerability management programs, and incident response procedures.
The security implications of this are not theoretical. Unauthorized infrastructure environments are disproportionately represented in enterprise breach investigations. They lack the patch management discipline of centrally managed systems. They are frequently configured with overpermissive access controls because the people deploying them are optimizing for functionality rather than security posture. They may store sensitive data — customer records, financial information, intellectual property — in environments that have not been assessed against applicable regulatory requirements.
The security team's challenge is compounded by the fact that they typically do not know these environments exist. Standard asset discovery processes identify infrastructure that has been provisioned through approved channels and registered in configuration management systems. Infrastructure deployed on a departmental credit card to a cloud account that IT did not create does not appear in those inventories. It is, by every operational measure, invisible until something goes wrong.
And when something goes wrong, the visibility problem becomes an incident response problem. The team tasked with containing a breach or investigating an anomaly is working with incomplete information about the environment involved. Response timelines extend. Containment is delayed. The investigation is conducted against a system whose architecture, access controls, and data inventory nobody in IT fully understands.
Compliance Exposure at the Department Level
For organizations operating in regulated industries — healthcare, financial services, critical infrastructure — the compliance implications of unauthorized infrastructure extend beyond internal policy violations. HIPAA, PCI DSS, SOX, and GLBA each impose requirements on the systems that process, store, or transmit regulated data. Those requirements apply regardless of whether the system was provisioned through IT or through a departmental initiative.
A business unit that deploys a cloud-based analytics environment containing patient data has created a HIPAA-covered system, whether or not it was intended as one. A finance department that routes payment data through an integration tool it deployed independently has potentially created PCI scope that was not included in the last assessment. The regulatory obligation does not pause because the infrastructure was not approved.
The compliance function's challenge is that it cannot assess what it cannot find. Annual audits and risk assessments are conducted against known infrastructure. The unauthorized stack is, by definition, not known. The exposure it creates accumulates silently until an audit, an incident, or a regulatory inquiry surfaces it — at which point the organization is explaining not just the vulnerability but the governance failure that allowed it to persist.
Why Traditional Centralization Is Losing the Argument
IT organizations that respond to shadow infrastructure primarily through restriction and enforcement are fighting a losing battle. The underlying demand — for faster provisioning, for specialized capabilities, for infrastructure that fits departmental workflows rather than enterprise standards — does not disappear when access is restricted. It finds alternative routes.
The organizations that are making meaningful progress against this problem are those that have reframed the question. Instead of asking how to prevent departments from deploying unauthorized infrastructure, they are asking what would make authorized infrastructure adequate to departmental needs.
This involves examining provisioning timelines honestly and reducing them where possible. It involves creating self-service capabilities that give business units operational flexibility within a governed framework. It involves building platform teams that treat internal departments as customers and compete on service quality rather than policy enforcement. And it involves acknowledging that some departmental requirements are genuinely specialized in ways that enterprise standards cannot accommodate — and building exception processes that are fast enough to be used rather than circumvented.
Visibility as the Starting Point
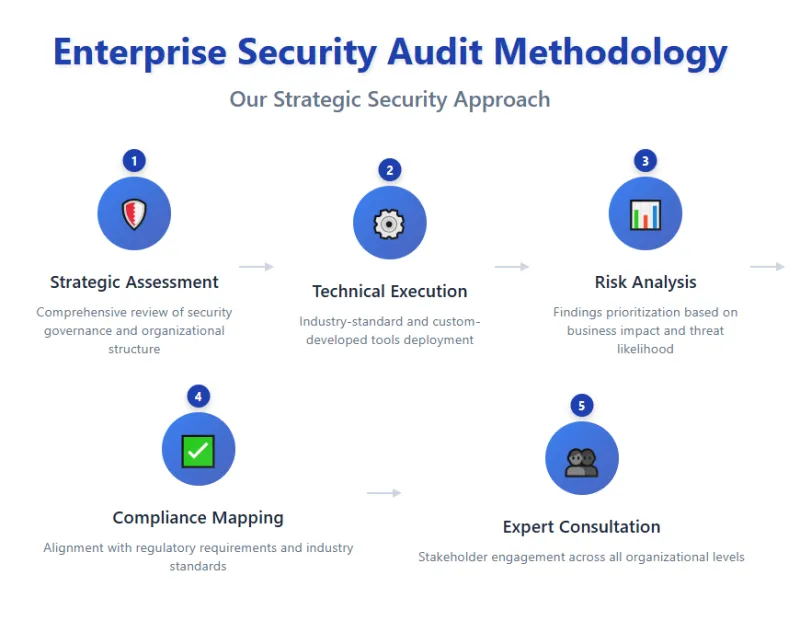
Before any of those structural changes can take effect, organizations need a realistic assessment of the unauthorized infrastructure that already exists. Cloud access security broker tools, cloud security posture management platforms, and network traffic analysis can surface environments that are not registered in official inventories. That discovery process is often uncomfortable — the scale of what is found typically exceeds what leadership expected.
But discomfort is not a reason to avoid the exercise. The infrastructure exists whether or not it has been discovered. The risks it carries are accumulating regardless of whether they have been assessed. Discovery is not the creation of a problem. It is the precondition for managing one.
The unauthorized stack is a symptom of a governance model that has not kept pace with the speed at which modern business units operate and the accessibility of modern infrastructure tools. Treating it as a policy violation addresses the symptom. Understanding why departments build what they build, and creating legitimate alternatives that are actually usable, is the only approach that addresses the cause.